-
OVERVIEW
-
SERVICES
-
MODELS
-
WHY CHOOSE US ?
-
OUR PROCESS
-
TECHNOLOGIES
-
FAQS
Code Audit at Saigon Technology
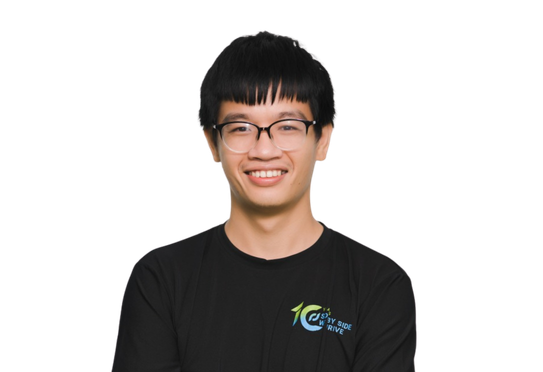
Findings checked by a named architect: Quy Truong, our Senior Solution Architect, leads each audit and reviews every scanner result by hand, so the findings you receive are ranked by what they put at risk in your product.
An audit that costs nothing: the code audit is our initial stack assessment, delivered at no charge. It ends in a work breakdown your team can price, schedule, or hand to any vendor.
Your source code stays protected: we sign an NDA before you share requirements and audit through read-only repository access, so nothing in your repository can be changed from our side.
Fixes on your terms: the audit is a standalone deliverable, so your engineers can work through the findings alone. If you want us on the fixes, the same team can stay, as on Turn It Blue Ads since 2022.
Who we build for
- Funded startups: find out whether an AI-built or prototype MVP can carry real users, then fix it at a fixed price.
- Mid-market companies: rank the risks in an inherited codebase before the next roadmap, then add fixes through staff augmentation.
- Software companies, SaaS vendors & agencies: vet code from a previous vendor before you take it on, then hire software developers who already know it.
- Enterprise teams: assess a long-running system before modernization, then staff the work through an ODC in Vietnam.
Our Code Audit Services
Code Quality and Maintainability Audit
Architecture and Scalability Review
Security and Dependency Review
AI-Generated and Prototype Code Audit
Pre-Handover Audit for Vendor Transitions
Case Studies: What We Found Before Changing the Code
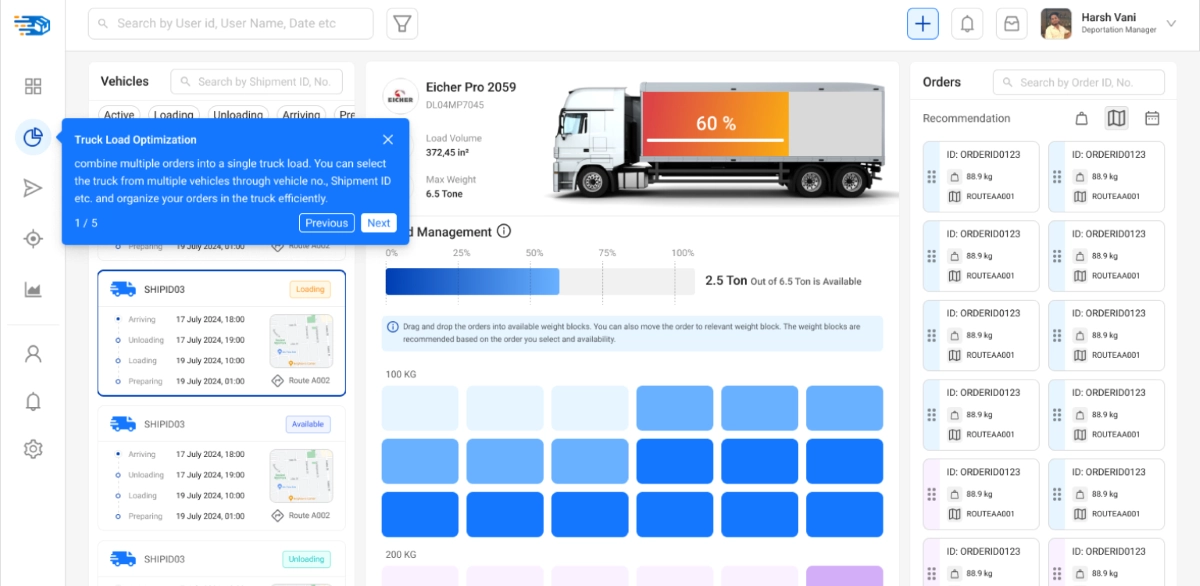
Merit Logistics ODC: Documenting an Inherited ERP Before Rebuilding It
- Challenge: a logistics business ran on a legacy ERP whose rules existed only in the code.Â
- What we built: ERP documentation, then maintenance and a rebuild checked by compare testing, then an Android check-in app. Read the Merit Logistics case study.Â
- Engagement / timeline: an ODC in Agile Scrum, with weekly effort reports.Â
- Outcome: the rebuild was tested against the legacy ERP before switchover.Â
- Stack: .NET Core, .NET Full, React JS, Angular
- Read the Merit Logistics case study
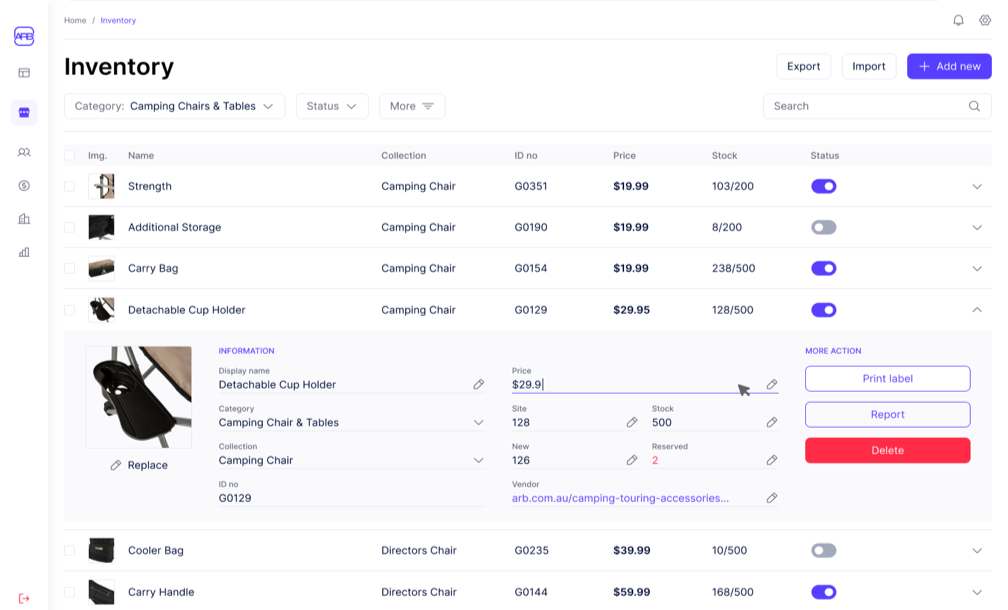
ARB Australia: Assessing an Unmaintained Codebase Before Choosing a Path
- Challenge: an unmaintained Ionic and Angular app had become slow and hard to staff, on a restricted budget.
- What we built: a feasibility study, a proof of concept, and a risk assessment, then one React Native codebase with CI/CD. Read the ARB Australia case study.
- Engagement / timeline: hourly terms, with a React Native developer and a part-time DevOps engineer.
- Outcome: the path was chosen on evidence from the proof of concept before the rewrite began.
- Stack: React Native, REST API, Azure DevOps, Oracle Cloud.
- Read the ARB Australia case study
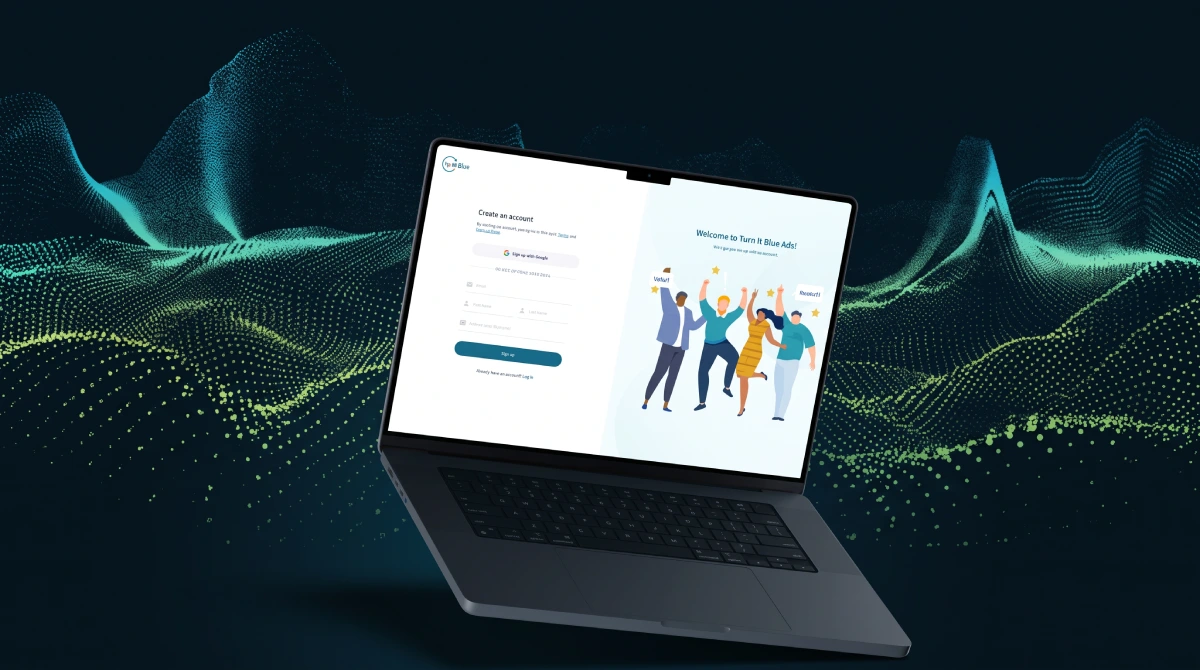
Turn It Blue Ads: Keeping Code Quality Up Through Five Years of Change
- Challenge: a programmatic advertising platform had to stay stable while its demand partners kept changing.
- What we built: a partner-agnostic backend with per-partner feature flags, plus code-quality work on the 2025 roadmap.
- Engagement / timeline: fixed price, then maintenance, enhancement, and a dedicated team, same team since 2022.
- Outcome: more than 130 maintenance items and more than 60 delivery items closed; partner reconfiguration takes under a minute.
- Stack: .NET Core, React, PostgreSQL, AWS, Hangfire.
- Read the Turn It Blue Ads case study
Get Your Codebase Risks Ranked Before Any Fix
Why Choose Saigon Technology for Code Audit Services?
A good independent code audit company has senior people read the code, ranks findings by business risk, says plainly when a rebuild isn't worth it, and protects the repository it reads. Saigon Technology builds every audit around those four tests.Â
Senior Architects Check Every Scanner Finding
Junior-led audits hand you raw tool output with no order. Our audits are senior-led at a published USD $22-$46/hr, and every reviewer passed three screening rounds: Talent Acquisition, Tech Lead, and HR.Â
A Ranked Work Breakdown at No Charge
Many audit reports end in a findings list nobody can schedule or price. Ours ends in a work breakdown structure ranked by risk and estimated task by task, at no charge, and your team can deliver every item in it without us.
We Say When a Rebuild Is Not Worth It
Some vendors steer every finding toward a rewrite they can sell. Our architects make a fix, keep, or replace call for each module, including when not to rebuild, and our guide on when to rebuild or refactor shows how we weigh it.
Your Source Code Stays Yours
An audit needs your whole repository, the asset a careless vendor can expose. We work under ISO 9001 and ISO 27001, both certified by BSI (UK), and the code, the findings, and all IP stay assigned to you.
The Team That Audits Can Stay to Fix It
Changing vendors after an audit means a new team relearns everything the auditors found. Saigon Technology ranked #10 in the Medium category of the Southeast Asia Best Workplacesâ„¢ in Technology 2026 (Great Place To Work), so the engineers who read your code tend to stay.
14+ Years · 400+ Developers · 850+ Projects · 350+ Clients · 3 Development Centers
Our direct audit engagements stay under NDA, so we show verifiable adjacent work in place of an audit metric we can't publish. The case studies above show how our teams read inherited code before changing it.
Start With a Two-Week Risk-Free Trial
If you want help with the fixes, start with a two-week risk-free trial on one workstream from the work breakdown before you commit. Continue through staff augmentation, a dedicated team, fixed price, an ODC, or BOT, whichever suits the remaining items.
Trusted by Global Clients
What Our Clients Say
Industries We Serve
Our Code Audit Process
Scoping call
We agree on your goals, your stack, and the decision the audit must support. Exit criterion: an approved scope.
NDA and access
We sign the NDA, and you grant read-only access to the repositories in scope. Exit criterion: access confirmed.
Automated scans plus manual review
Vulnerability scanning and code analysis tools cover the whole repository, then architects build it, run the tests, and read the critical paths. Exit criterion: a findings list.
"A scanner reports every rule a file breaks and weighs them all the same. I read the code to find the few that can stop a release, expose data, or block the next feature, and those lead the work breakdown." Quy Truong, Senior Solution Architect, Saigon Technology
Ranked findings and work breakdown
Each issue is rated critical or non-critical and estimated in a remediation roadmap. Exit criterion: an approved work breakdown.
Walkthrough with the architect
Quy Truong takes your team through the detailed report and its practical recommendations. Exit criterion: a fix, keep, or replace decision per module.
Post-audit consultation
Your team fixes the findings alone, or our software maintenance and support team takes them on. Exit criterion: the first fix ships.
Our Insights
FAQs
How much do code audit services cost?
Our code audit services cost nothing at the start: the audit is our initial stack assessment, and it ends in a ranked work breakdown. If you then want us on the fixes, the rate is $22-$46/hr and projects start from $5,000, priced from the work breakdown you reviewed.Â
How long does a code audit take?
A code audit takes as long as your repository's size, documentation, and number of integrations require, so we confirm the timeline on the scoping call. A small, documented codebase moves faster than a legacy system with many integrations and few tests, and the estimate is agreed before access starts.
Should your own team or an independent firm audit your code?
Your own team should review code every sprint, and an independent firm should audit it before a big decision: a vendor change, a funding round, a scale-up, or a technology stack upgrade. An independent audit brings objectivity, because the reviewers have no past choices in the codebase to defend.
How do you protect our source code during an audit?
We sign an NDA before you share requirements, work through read-only repository access, and operate under ISO 27001 certified by BSI, with code and IP assigned to you. HIPAA and PCI-DSS requirements are met where the workload needs them, and GDPR is applied as standard when an engagement handles EU personal data.
What is the difference between a code audit and a code review?
A code review checks individual changes before they merge, usually by teammates, while a code audit examines the whole codebase at one point in time with outside reviewers. The audit ranks architecture, security, and technical debt risks across the system; our guide to AI code review covers the review side.
Can you audit AI-generated or prototype code?
Saigon Technology audits AI-generated and prototype code with its standard checks, plus tests for patterns AI coding tools tend to produce: duplicated logic, missing input validation, exposed credentials, and tests that pass without checking behavior. You learn which parts are ready for production and which need work first.
What happens after the audit?
After the audit, you own a ranked work breakdown and decide who delivers it. The audit is a standalone deliverable, so your team can fix findings alone, or Saigon Technology can take them on through staff augmentation, a dedicated team, or a fixed-price project, with post-audit consultation from the same architect.
What technology stacks do you audit?
We audit frontend and backend code on the stacks our 400+ developers build with every day, including legacy codebases on older framework versions and open-source components with license terms to check:
| Area | What we work with |
|---|---|
| Back end | .NET, Java, Node.js, Python, Ruby on Rails |
| Front end | React, Angular, Vue.js, TypeScript |
| Mobile | iOS, Android, React Native, Flutter |
| Cloud and DevOps | AWS, Azure, Google Cloud, Docker, Kubernetes |